Quick summary for busy business owners.
- Using AI for company work can be appropriate, but the tool, account type, information and business purpose must all be approved.
- Personal AI accounts give employers less control over access, settings, retention, sharing and employee offboarding.
- Removing a customer name may not truly anonymise the data when the remaining details can still identify the person.
- Business-grade AI services improve control, but they do not replace staff rules, access management and human review.
- A controlled AI workflow can send only the necessary data, enforce permissions and require approval before important actions.
One morning, a business owner proudly told me that his staff had become very productive with ChatGPT.
“Now they use it to reply to customers, prepare quotations and summarise documents,” he said.
Very good. Productivity increased.
Then I asked one small, irritating question:
“Which ChatGPT account are they using?”
He looked at me.
I looked at him.
Somewhere in the office, an employee was probably pasting a customer spreadsheet into a free personal account.
AI adoption had arrived.
The company policy was still looking for parking.
This is becoming a serious question for Singapore businesses: Is it safe for employees to put company or customer data into ChatGPT, Claude, Gemini or another AI tool?
The short answer is: sometimes—but only when the company has approved the particular tool, account type, information and business purpose.
Sensitive business information should not be pasted casually into somebody’s personal AI account just because the answer comes back quickly and looks clever.
Singapore companies are adopting AI faster than they are securing it
On 10 November 2026, a Singapore report highlighted a rather interesting mismatch.
More than half of the organisations surveyed were already using AI, but they had implemented, on average, fewer than 40% of the relevant AI cybersecurity measures. The SUTD summary of the Singapore findings described businesses as adopting AI first and adding safeguards later.
In other words, many companies boarded the AI bus first and asked where it was going later.
The wider cyber environment is not exactly peaceful either. The Cyber Security Agency of Singapore reported that almost nine in ten surveyed organisations encountered at least one cybersecurity incident in 2025.
Employees are already using AI for customer replies, proposals, research, spreadsheets and administrative work. Meanwhile, some employers are still arranging their first “AI transformation strategy meeting,” complete with PowerPoint slides and refreshments.
The business may think it has not adopted AI.
Its employees may disagree.
This unofficial use of artificial intelligence is sometimes called shadow AI: staff use AI services without formal company approval, supervision or security controls.
The staff member is not necessarily behaving maliciously. He may simply be trying to finish three hours of work before lunch.
The problem is that convenience can quietly move customer data, company documents and confidential information outside the systems the business controls.
Is company data safe in ChatGPT?
Company data can be used with ChatGPT more safely when the organisation uses an approved business account, understands the applicable data terms, restricts what employees may submit and creates proper access and review controls.
However, “We use ChatGPT” is not enough information.
A personal ChatGPT account and a managed ChatGPT Business or Enterprise workspace may show the same logo, but they do not offer identical privacy commitments or administrative controls.
OpenAI states that information submitted through ChatGPT Business, ChatGPT Enterprise and its API platform is not used to train its models by default.
For personal ChatGPT accounts, users can manage whether new conversations are used for model improvement through their data-control settings.
That distinction matters, but it is not the whole answer.
Turning off model training does not automatically create a complete company data-governance programme.
The information is still being processed by an external service. The business must still consider access, retention, employee behaviour, connected applications, personal data, contractual responsibilities and what happens when somebody leaves the company.
Buying a business subscription is helpful.
It is not holy water.
Your staff may already be using personal AI accounts
When I help businesses study their workflows, I ask annoyingly simple questions.
How does an enquiry arrive? Who copies it into the system? Where is the customer file stored? Who prepares the quotation? What happens after the salesperson presses Send?
These questions often reveal that the official workflow and actual workflow are distant relatives who meet only during Chinese New Year.
Management may believe staff are using an approved company system.
The staff may actually be copying information into Excel, sending it through WhatsApp, uploading it to a free online converter and asking ChatGPT to summarise it.
Why?
Because the official system takes 14 clicks, two approvals and one small prayer.
The employee is trying to get work done.
That is why completely banning AI often fails. Staff may continue using it quietly because it saves time.
A better solution is to understand what they are doing, provide approved tools and establish practical boundaries.
What should never be pasted casually into an AI tool?
Not all information carries the same level of risk.
Asking an AI tool to improve a generic public marketing paragraph is quite different from uploading an Excel file containing 2,000 customer records.
Generally lower-risk uses
- Brainstorming public marketing ideas
- Rewriting non-confidential text
- Improving a publicly available job advertisement
- Summarising information already published on your website
- Creating a generic meeting agenda
- Checking the tone of an ordinary email without personal details
Higher-risk information
- Customer names and contact details
- NRIC and passport information
- Employee and payroll records
- Medical information
- Bank and payment details
- Confidential contracts
- Unreleased prices and business plans
- Passwords, security tokens and API keys
- Complete customer databases
- Proprietary source code
- Internal complaints or disciplinary records
- Legal advice and privileged communications
My simple rule for non-technical business owners is:
If you would not paste it into a public WhatsApp group, do not paste it into an unapproved AI tool.
This rule is intentionally conservative.
But it is much easier to remember than a 47-page information-security policy that everybody will acknowledge and nobody will read.
Removing the customer’s name may not be enough
Some employees try to anonymise information by deleting the person’s name.
That is a good start, but it may not be enough.
Suppose a customer’s name is removed, but the prompt still contains her company, job title, address, transaction date, amount involved and a detailed description of her unusual complaint.
Congratulations. Her name has disappeared, but anybody familiar with the incident may still identify her.
Proper anonymisation requires removing or generalising the collection of details that could identify a person.
The Personal Data Protection Commission provides guidance on anonymisation and using personal data in AI systems. Its guidance discusses appropriate purposes, meaningful consent or applicable exceptions, safeguards and transparency.
This article is not legal advice, and businesses dealing with regulated or high-risk data should seek appropriate professional guidance.
However, one principle is easy to understand: if your company collects somebody’s personal data for one purpose, do not casually send it into an unrelated AI service without first determining whether that use is permitted and properly controlled.
What about ChatGPT Business, Enterprise and APIs?
Business-grade AI services can provide stronger protections and company-level controls.
For example, a managed workspace may offer business data excluded from model training by default, centralised user management, better control over staff access, stronger privacy commitments and easier removal of access when an employee leaves.
An API-based system can provide even more control over the workflow.
Instead of allowing employees to paste entire documents manually, a custom system can send only the necessary fields, remove unnecessary identifiers, record the request and require human approval before acting on the result.
But business plans still require governance.
The company must decide who may use AI, what types of data they may submit, which applications may be connected, how long information should be retained, which results require human approval and who checks the answers.
The correct question is not merely, “Does this AI company train on our information?”
It is also, “Do we know what our own staff are sending, why they are sending it and what happens next?”
The danger is not only what goes into AI
Most conversations about AI security focus on the prompt.
But the output can also create business problems.
An AI tool may produce an incorrect calculation, fictional legal requirement, inaccurate technical explanation, made-up source, unauthorised promise, insecure code or confident but completely wrong recommendation.
AI is excellent at producing convincing language.
Unfortunately, convincing and correct are not the same thing.
I have been developing business software for decades. One lesson remains consistent whether we are discussing a human programmer, an Excel formula or an AI agent: the more power a system has, the more carefully its permissions and checks must be designed.
If an AI system can only draft an email, a mistake may be embarrassing.
If it can send the email, alter customer records, approve a refund and update the accounting system, a mistake can become tomorrow morning’s emergency meeting.
Singapore’s updated Model AI Governance Framework for Agentic AI recommends bounding risks, keeping humans meaningfully accountable, applying technical controls and training users.
That sounds very grand, but the everyday principle is simple: do not give an AI agent unlimited authority merely because it completed a demo successfully.
Even the office intern gets supervision on the first day. Your new digital robot should not immediately receive the keys to the building.
Do not ban AI blindly
Some employers respond to these risks by banning every AI service.
I understand the instinct.
But an absolute ban may create a different problem: staff continue using AI privately because it helps them finish their work.
Then the business has both AI usage and no visibility.
Very efficient.
A more practical approach is to identify the genuine use cases: improving English in customer replies, summarising long emails, preparing proposal drafts, categorising support requests, extracting information from documents or converting meeting notes into action lists.
These are reasonable business needs.
The company can then provide approved tools and teach employees how to remove unnecessary personal or confidential information.
The aim is not to stop productivity.
It is to prevent productivity from becoming evidence in a future incident report.
A practical seven-step AI safety plan for SMEs
You do not need to form an International Artificial Intelligence Security Committee with 27 members and a ceremonial chairman.
Start with seven practical actions.
1. List the AI tools currently being used
Ask staff openly which services they use for work. Include ChatGPT, Claude, Gemini, Copilot, Perplexity, image generators, meeting transcription services and AI features inside existing software.
Do not begin the discussion like an interrogation. You want an accurate list, not a competition to see who can clear browser history fastest.
2. Identify what information enters each tool
For each service, ask what is uploaded, whether it contains personal or confidential information, whether that information is necessary and whether a reduced or anonymised version could work.
This simple data map is often more useful than buying another expensive security dashboard.
3. Approve official company accounts
Where AI genuinely helps the business, consider providing managed business accounts instead of allowing employees to use personal accounts.
Keep company work inside company-controlled workspaces, and ensure access can be removed when an employee leaves.
4. Create a one-page AI acceptable-use policy
Do not begin with a giant document written like an international treaty.
Start with one page stating which tools are approved, what information is prohibited, which tasks require permission, when outputs must be checked and who staff should ask when uncertain.
A short policy employees understand is more useful than a long policy decorating the shared drive.
5. Separate harmless, sensitive and prohibited data
A simple traffic-light system works well:
- Green: Public and non-confidential information.
- Amber: Internal information requiring approval or anonymisation.
- Red: Passwords, identity documents, payment information, medical records, confidential contracts and regulated personal data.
Staff do not need to memorise every possible scenario. They need a clear decision path.
6. Keep humans responsible for important decisions
Require human review before AI-generated content is sent to customers, changes a price, approves a refund, modifies important records, produces legal or financial advice, makes hiring recommendations or triggers payments.
The AI can prepare the work. A responsible human should approve high-impact decisions.
7. Review access and integrations regularly
AI tools increasingly connect to email, cloud drives, customer databases and business applications. Review connected applications, shared conversations, former employee accounts, publicly shared assistants, API credentials, automation permissions and activity logs.
Yesterday’s harmless chatbot may become tomorrow’s agent with access to half the company.
Software enjoys receiving new powers. It rarely sends management a polite reminder to review them.
When custom AI automation is safer than copy and paste
Suppose employees repeatedly copy customer enquiries from email into an AI tool, ask it to prepare a response and then paste the answer back.
That may save time, but the process is inconsistent and difficult to supervise.
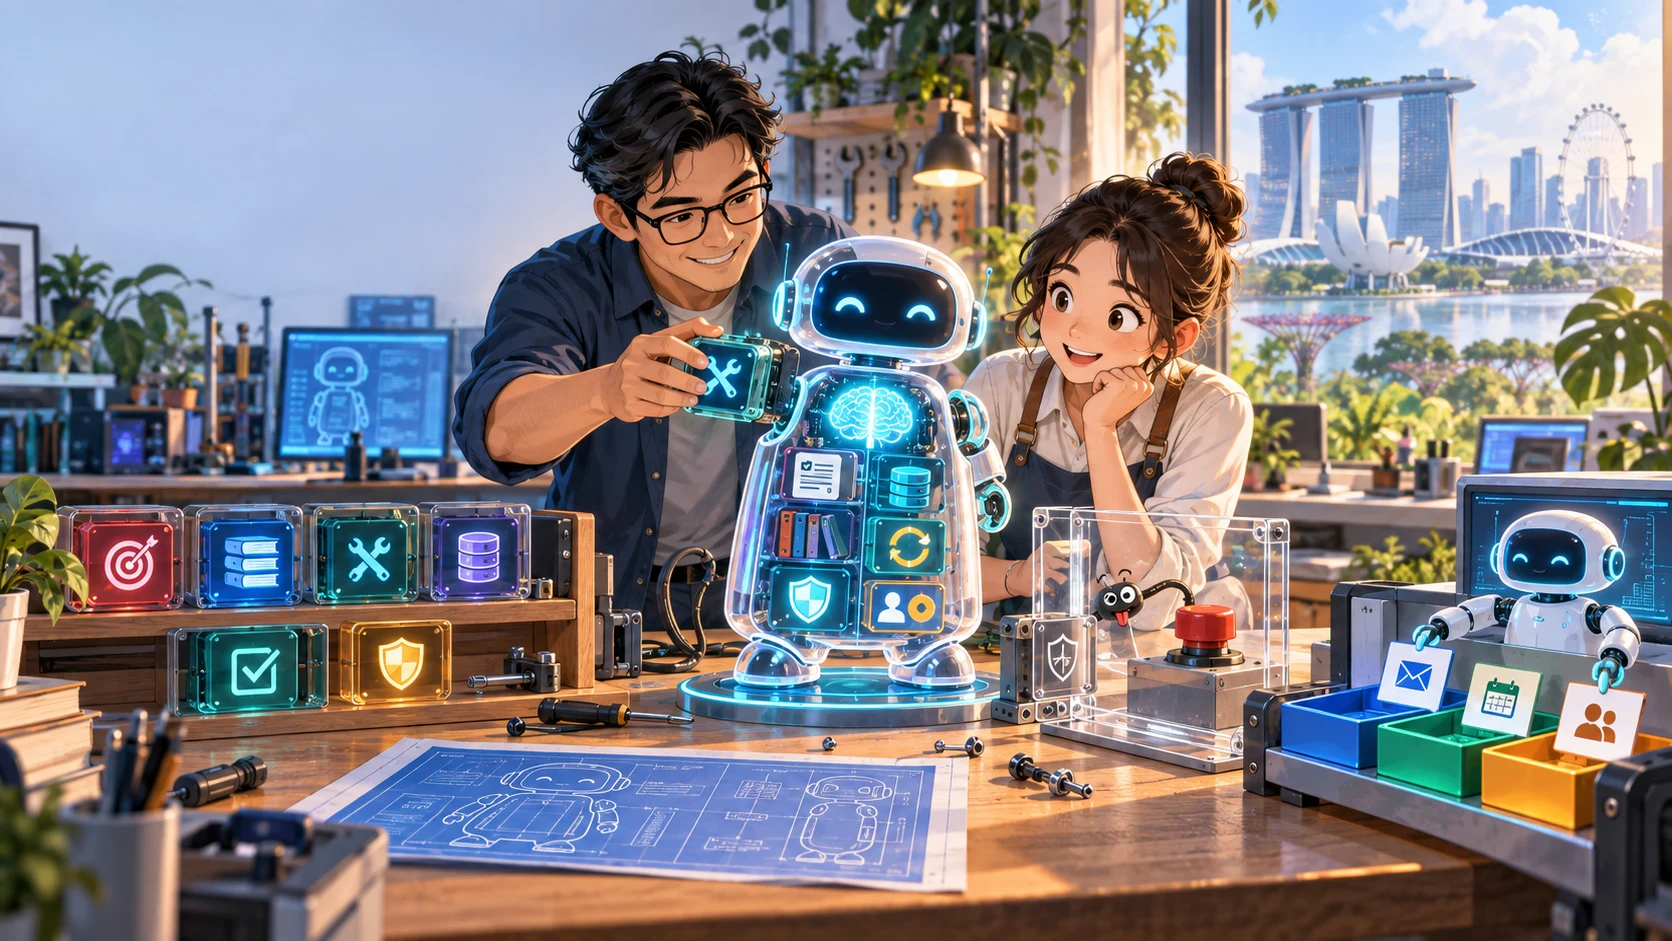
A controlled AI workflow can be designed to:
- Read only the information needed for the task
- Remove unnecessary identifiers
- Use an approved business API
- Restrict access according to staff roles
- Record what information was processed
- Apply a fixed business prompt
- Flag uncertain answers
- Require human approval before sending
- Prevent certain actions completely
For example, an AI enquiry assistant does not necessarily need access to the full customer database.
It may only need the customer’s current question, relevant product details and the company’s approved response guidelines.
Good software does not give everybody access to everything.
Good AI automation should follow the same principle.
This is where an experienced developer becomes useful.
The difficult part is not connecting an AI model to a form. That part can be completed quickly.
The difficult part is understanding how the business actually works, which information is genuinely required, where human approval belongs, what should happen when AI is uncertain and which actions must never be automated.
AI is only one component.
The workflow is the real system.
What if the company has no AI policy today?
Do not panic.
Also, do not pretend the problem does not exist because nobody has reported an incident.
Begin with a friendly internal question:
“Which AI tools are helping you with your work, and what do you normally put into them?”
The answers may surprise you.
Once you understand the actual usage, create basic rules, move legitimate work into approved accounts and stop sensitive information from entering unsuitable tools.
Then decide whether any repeated process deserves a controlled custom workflow.
You do not need to solve the entire future of artificial intelligence by Friday.
You need to stop unmanaged use and establish responsibility.
Need help reviewing your company’s AI workflows?
Getcha Solutions can review how your staff currently use AI, identify sensitive information in the workflow, recommend appropriate controls and build safer automation around your actual business process.
This may involve a managed AI workspace, a simple acceptable-use structure, custom API integration, permission controls or a human approval step. Sometimes the correct recommendation is not to automate a particular task at all.
Explore AI automation for Singapore SMEs, see the wider Getcha development services, or contact me for an AI workflow and data-safety review.
Final thoughts
AI is not waiting for management to finish discussing whether the company should adopt it.
Your employees may already be using it.
That is not automatically bad. AI can save time, improve communication and reduce repetitive administrative work.
But a customer spreadsheet should not be treated like a harmless prompt.
The biggest risk is often not the AI model itself.
It is the absence of clear responsibility.
The boss assumes IT is handling it. IT assumes management approved it. Management assumes staff know what is confidential. Staff assume that because the website has a professional logo, everything must be safe.
Once again, everybody is involved and nobody is responsible.
The solution is not panic, and it is not blindly banning every useful tool.
Find out what is already happening. Approve suitable services. Set simple rules. Restrict sensitive data. Keep humans responsible for important decisions. Build controlled workflows where repeated copying and pasting has become part of the business.
If you checked today, would you know what company and customer information your staff are putting into AI?
What is your company’s current approach? Do you allow staff to use AI freely, provide approved business accounts, or quietly hope everybody uses common sense? Share your experience when I post this article—or contact Getcha Solutions if you want help reviewing the workflow properly.
Common questions about this topic.
Is it safe to enter company information into ChatGPT?
It depends on the information, account type, settings, business purpose and company policy. Public or non-confidential information is generally lower risk. Sensitive, personal or confidential information should not be submitted unless the business has assessed and approved the tool and usage.
Does ChatGPT use business data for training?
OpenAI states that inputs and outputs from ChatGPT Business, ChatGPT Enterprise and its API platform are not used to train its models by default. Personal workspaces have separate data controls, so businesses should check the current terms and settings of the exact service and plan being used.
Can staff use personal ChatGPT accounts for work?
A business should avoid relying on personal AI accounts for confidential work. Personal accounts reduce the organisation’s control over access, settings, retention, sharing and removal of access when an employee leaves.
Can I paste customer data into ChatGPT under Singapore’s PDPA?
Organisations remain responsible for how they collect, use, disclose and protect personal data. Whether a specific use is permitted depends on its purpose, consent or applicable exceptions, safeguards and other circumstances. Obtain appropriate legal or data-protection advice for sensitive or regulated uses.
Is removing a customer’s name enough to anonymise the data?
Not always. A combination of company, job title, address, transaction details or unusual circumstances may still identify the person. Proper anonymisation considers the complete dataset rather than only the name field.
Should my company ban ChatGPT and other AI tools?
A total ban may be appropriate in some high-risk environments, but it can also drive useful AI activity underground. Many SMEs will benefit more from approved tools, clear data rules, staff education and controlled workflows.
Is ChatGPT Business completely risk-free?
No online service is completely risk-free. A business workspace can provide stronger privacy commitments and administrative controls, but the organisation must still manage users, data, integrations, retention, sharing and human review.
What is shadow AI?
Shadow AI refers to employees using AI tools for work without formal organisational approval, supervision or governance. It is similar to shadow IT, where staff adopt software outside official company processes.
Can Getcha Solutions help a Singapore SME use AI safely?
Yes. Getcha Solutions can review existing workflows, identify practical AI use cases, assess where sensitive information is involved and build controlled AI automation around the organisation’s real business processes.